Updated: 30 March, 2026
27 March, 2026
Imagine you are a software vendor selling a banking app in 2026. Are you a critical service provider or a product manufacturer? The answer determines whether you must answer to the Digital Operational Resilience Act (DORA) or the Cyber Resilience Act (CRA). While they share a common goal of digital security, the fundamental difference is simple: DORA regulates the resilience of the organization, while the CRA regulates the safety of the product.
It is now March 2026, and the “planning phase” for EU compliance is officially over. DORA is no longer a checklist for the future; it is a live operational requirement enforced across the entire financial sector. Meanwhile, the CRA is rapidly approaching its first major milestone, with mandatory vulnerability reporting just six months away.
For many businesses, these two laws are currently on a collision course. If you sell digital tools to banks, you are caught in the middle of a “double jeopardy” zone. You must prove your company’s operational stability to satisfy your clients’ DORA audits, while simultaneously proving your software’s technical integrity to meet CRA standards. This guide breaks down how to navigate this overlap and turn regulatory pressure into a strategic advantage.
Key Takeaways
- While DORA secures the operational resilience of financial organizations, the CRA mandates the cybersecurity and safety of the digital products those entities use.
- ICT providers for the financial sector occupy a unique “collision zone,” requiring them to comply with DORA’s organizational standards and the CRA’s product requirements simultaneously.
- Organizations must synchronize their incident response teams to manage DORA’s 4-hour major incident window alongside the CRA’s 24-hour mandate for reporting actively exploited vulnerabilities.
- The CRA-mandated Software Bill of Materials (SBOM) acts as a critical digital nutrition label, helping financial firms satisfy DORA’s strict requirements for third-party risk management.
- Non-compliance poses a major financial threat, with penalties ranging from DORA’s supervisory interventions to the CRA’s hard fines of up to 2.5% of global annual turnover.
What is the Cyber Resilience Act (CRA) and the Digital Operational Resilience Act (DORA)?
Imagine you are a software vendor selling a banking app in 2026. Are you a critical service provider or a product manufacturer? The answer determines whether you must answer to the Digital Operational Resilience Act (DORA) or the Cyber Resilience Act (CRA). While they share a common goal of digital security, the fundamental difference is simple: DORA regulates the resilience of the organization, while the CRA regulates the safety of the product.
It is now March 2026, and the “planning phase” for EU compliance is officially over. DORA is no longer a checklist for the future; it is a live operational requirement enforced across the entire financial sector. Meanwhile, the CRA is rapidly approaching its first major milestone. These laws are currently on a collision course, creating a “double jeopardy” zone for businesses that sit in the middle.
DORA: The Organizational Fortress
DORA is a sector-specific regulation designed to ensure the financial system can withstand significant ICT disruptions. Rather than focusing on a single tool, DORA requires entities to build a comprehensive “fortress” around their entire operation.
- Systemic Stability: It ensures that if one bank is attacked, the entire European financial market does not collapse.
- Operational Control: It mandates how companies identify risks, detect threats, and recover from successful breaches.
- Active Oversight: Financial regulators have direct power to audit the internal processes of banks and their most critical technology partners.
The CRA: The Product Shield
The Cyber Resilience Act is a horizontal law. This means it applies to almost all connectable software and hardware sold in the EU, regardless of the industry. While DORA looks at how a business is run, the CRA looks at how a product is built.
- Security by Design: It forces manufacturers to integrate security into every stage of the development process.
- Lifecycle Protection: Manufacturers must remain responsible for fixing flaws in their products for years after the initial sale.
- Transparency: It requires technical proof that a product is safe to use before it can legally enter the EU market.
In 2026, these regulations act as two sides of the same coin. The CRA provides the secure tools, while DORA ensures the organizations using them remain standing. Understanding this interplay is the first step toward a successful compliance strategy.
Who Must Comply with the Cyber Resilience Act (CRA) and Digital Operational Resilience Act (DORA)?
Identifying whether your organization falls under DORA, the CRA, or both is essential for your 2026 strategy. While these regulations often overlap, they target different operational areas. DORA primarily secures the financial entity, whereas the CRA secures the digital product.
The Scope of DORA: Financial Entities and Partners
DORA applies to a broad range of institutions within the financial ecosystem. If your company processes transactions or manages capital, you likely fall under its mandate.
- Financial Institutions: This group includes traditional banks, credit unions, and investment firms.
- Payment & Crypto Services: Payment institutions and crypto-asset service providers must adhere to these rules.
- Insurance & Pensions: Insurance companies and occupational retirement providers are also in scope.
- Critical ICT Providers: Organizations providing cloud services or data analytics to banks are regulated directly.
The Scope of the CRA: Digital Product Manufacturers
The CRA casts a much wider net across all industrial sectors. It applies to any “product with digital elements” that connects to a device or network.
- Hardware Manufacturers: This includes makers of smart sensors, routers, and industrial servers.
- Software Developers: Vendors of operating systems, mobile applications, and enterprise software must comply.
- Importers and Distributors: Companies bringing digital products into the EU market must verify their compliance.
For a deeper dive into the specific entities covered by the product regulation, see this guide on who needs to comply with the Cyber Resilience Act.
The “Collision Zone”: Who is Caught in the Middle?
The most complex challenge in 2026 belongs to ICT providers for the financial sector. If you sell a banking application or a security tool to a financial entity, you occupy the middle ground.
Consequently, you are viewed as an ICT service provider under DORA and a software manufacturer under the CRA. You must satisfy your client’s DORA audit requirements while maintaining your own CRA technical documentation. Successfully managing this “double jeopardy” requires a unified approach to security evidence.
The CRA vs. DORA Comparison: Mapping Objectives, Requirements, and Key Differences
While both laws aim to strengthen the EU’s digital defenses, they operate through different mechanisms. DORA is designed to protect the financial system from operational failures. In contrast, the CRA ensures that the individual products entering that system are inherently secure.
Resilience vs. Security-by-Design
The fundamental difference lies in their primary objectives.
- DORA (Financial Resilience): This regulation focuses on availability and continuity. The goal is to ensure that a financial institution can withstand, respond to, and recover from all types of ICT-related disruptions.
- CRA (Product Integrity): This act focuses on security-by-design. The goal is to reduce vulnerabilities in hardware and software at the manufacturing stage, ensuring products remain secure throughout their lifecycle.
Comparing Core Requirements
Compliance looks very different depending on which regulation you are addressing.
- DORA Mandates: Financial entities must build an ICT risk management framework. They must also conduct regular resilience testing and manage third-party risk through strict contractual requirements.
- CRA Mandates: Manufacturers must perform formal cybersecurity risk assessments. They are required to provide security updates for at least five years and must produce a Software Bill of Materials (SBOM).
The “Lex Specialis” Relationship
In legal terms, DORA acts as lex specialis for the financial sector. This means that for financial institutions, DORA’s specific rules often take precedence over more general regulations.
However, this does not mean you can ignore the CRA. While DORA governs how a business operates, the CRA governs the tools that business uses. If a software product used by a bank lacks CRA-mandated security features, the bank faces higher operational risk. This could eventually lead to a DORA compliance failure.
Essentially, the CRA creates the “floor” for product security. DORA then builds the “walls” of organizational resilience on top of it. Together, they provide a comprehensive defense for the European digital economy.
You are exactly right. While the section compares the duration of the reporting windows (the 4-hour vs. 24-hour clocks), the link is most helpful when discussing when these specific reporting obligations actually start.
Moving the link to the final paragraph provides the reader with the “big picture” timeline right after they’ve learned about the technical deadlines.
Reporting Timelines: DORA’s Operational Incident Windows vs. CRA’s Vulnerability Mandates
In 2026, the speed of your response determines your compliance. DORA and the CRA both enforce strict reporting windows, but they trigger under different circumstances. DORA focuses on operational failures, while the CRA targets product-level vulnerabilities.
DORA: The 4-Hour Response Window
DORA requires financial entities to report “major ICT-related incidents” with extreme urgency. If your organization suffers a significant outage or breach, the clock starts immediately upon discovery.
- Initial Notification: You must submit this within 4 hours of classifying the incident as major, and no later than 24 hours after becoming aware.
- Intermediate Report: A detailed update is due within 72 hours of the initial notification.
- Final Report: You must provide a full root-cause analysis within one month.
The CRA: The 24-Hour Vulnerability Clock
The CRA introduces a new mandate for reporting actively exploited vulnerabilities. This requirement is vital for manufacturers to understand, as it applies to products even if they were shipped before the law’s full implementation.
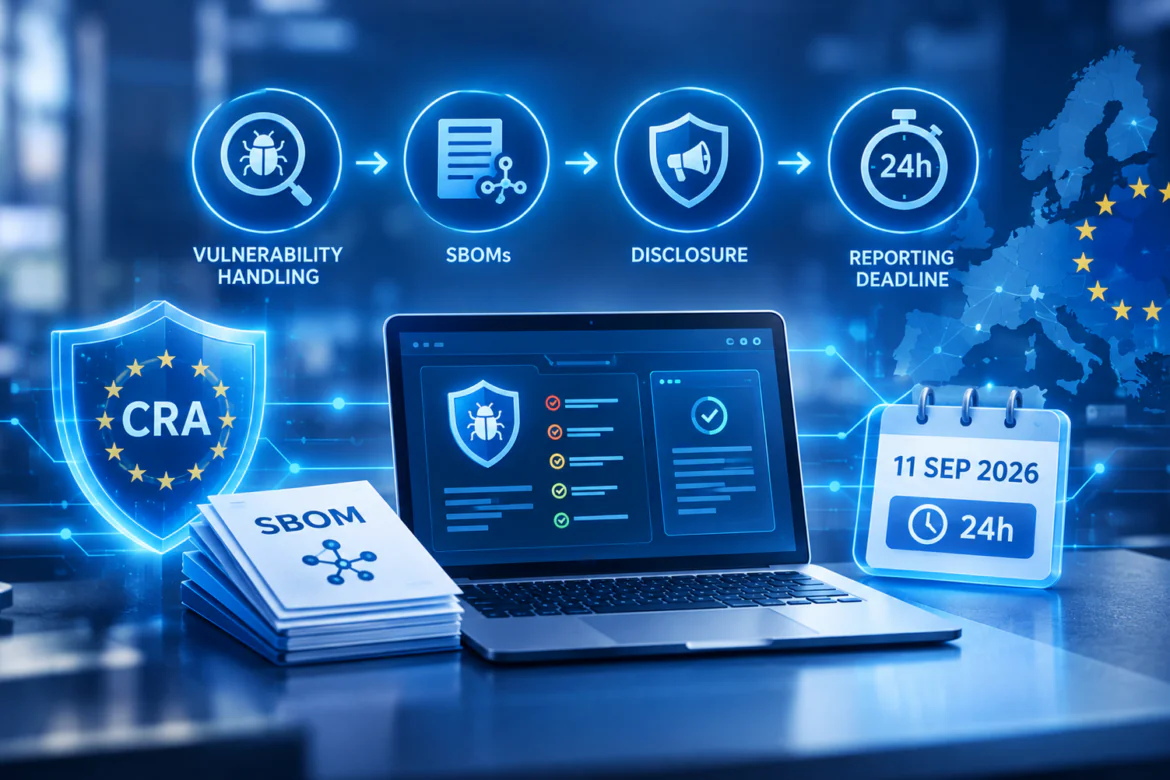
- Early Warning: You must notify ENISA within 24 hours of becoming aware of an actively exploited vulnerability.
- Vulnerability Notification: A more comprehensive report is required within 72 hours.
- Final Report: This must be submitted within 14 days of a security patch or corrective measure becoming available.
Managing the Collision Risk
The biggest challenge for ICT providers is the 24-hour overlap. A single security breach could be classified as both a “major incident” under DORA and an “exploited vulnerability” under the CRA. Consequently, your incident response team must be prepared to file multiple reports to different authorities simultaneously.
Missing these windows can lead to heavy fines and supervisory intervention. Because Article 14 of the CRA, which covers these reporting duties, becomes enforceable on September 11, 2026, your infrastructure must be ready soon. For a complete breakdown of all enforcement milestones, see this guide on by when you need to comply with the Cyber Resilience Act.
The Supply Chain Handshake: Using the CRA’s SBOM to Simplify DORA’s Third-Party Risk Management
DORA mandates that financial institutions manage their supply chain with intense scrutiny. Meanwhile, the CRA forces manufacturers to provide a Software Bill of Materials (SBOM) for every digital product. Consequently, these two requirements create a perfect “handshake” between banks and their software vendors.
The SBOM: A Digital Nutrition Label
Under the CRA, every software product must include an SBOM. This document acts as a digital nutrition label, listing all components and their top-level dependencies. This transparency directly solves one of DORA’s biggest headaches: third-party risk visibility.
How the CRA Simplifies DORA Compliance
Financial entities can use a vendor’s CRA-mandated technical file to satisfy several DORA requirements.
- Enhanced Due Diligence: Banks no longer need to rely solely on vague questionnaires. Instead, they can inspect the SBOM to verify if a vendor uses insecure or outdated libraries.
- Vulnerability Tracking: When a new vulnerability emerges, the SBOM allows a bank to identify immediately if its critical systems are at risk.
- Standardized Evidence: Because the CRA requires a machine-readable SBOM, financial entities can automate their vendor risk assessments.
- Contractual Assurance: DORA requires specific security clauses in ICT contracts. A vendor that is already CRA-compliant can provide the necessary technical evidence with ease.
A Competitive Edge for Vendors
In 2026, compliance is a powerful sales feature. Vendors who proactively share their SBOMs make it significantly easier for banks to pass their own DORA audits. By aligning your CRA output with your client’s DORA needs, you transform a regulatory burden into a competitive advantage.
Therefore, do not view these regulations as separate hurdles. Treat the CRA as the technical foundation that makes your DORA partnership possible.
CRA and DORA Fines for Non-Compliance
Ignoring compliance is not just a security risk. It is a significant financial risk. Both DORA and the CRA empower regulators to impose heavy penalties. However, their enforcement styles differ significantly.
CRA Penalties: The Hard Tiers
The Cyber Resilience Act establishes specific, tiered administrative fines. These deterrents target manufacturers, importers, and distributors.
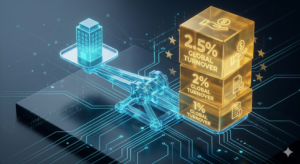
- Essential Violations: Failing to meet essential security requirements or reporting duties can lead to fines of €15 million or 2.5% of worldwide turnover.
- General Obligations: Violating duties like documentation or CE marking rules can result in fines of €10 million or 2% of turnover.
- Misleading Information: Providing incorrect data to authorities carries a penalty of up to €5 million or 1% of turnover.
For a detailed breakdown of these penalties and how they apply to different business sizes, see this guide on CRA fines.
DORA Penalties: Supervisory Intervention
Unlike the CRA’s fixed caps, DORA grants national authorities broad powers to compel compliance. The focus is often on continuous pressure rather than a single hit.
- Periodic Penalty Payments: Regulators can impose daily fines to force a financial entity to fix a vulnerability. For critical ICT providers, these daily fines can reach 1% of average daily worldwide turnover.
- Public Sanctions: Authorities often issue public statements naming non-compliant entities. This causes severe reputational damage in the finance sector.
- Cease and Desist Orders: Regulators can order the permanent cessation of practices that violate the regulation.
Determining the Fine Amount
In both regimes, regulators consider several factors before issuing a fine. They evaluate the severity of the breach and the duration of non-compliance. They also assess the entity’s level of cooperation. Crucially, they look at the financial strength of the organization.
Consequently, 2026 is the year to move from planning to proving. Ensure your evidence trails are complete to avoid these costly interventions.
Summary: A Unified Compliance Strategy for the Cyber Resilience Act (CRA) and DORA
In March 2026, the distinction between “product security” and “operational resilience” is rapidly disappearing. DORA is now the standard for how financial firms operate. Simultaneously, the CRA is becoming the mandatory standard for the tools those firms use. To thrive in this environment, you must stop treating these regulations as separate projects.
The Power of a Unified Framework
The most successful organizations are moving away from siloed compliance teams. Instead, they are adopting a unified evidence strategy. This approach ensures that a single security control can satisfy multiple regulatory requirements at once.
- Centralize Evidence: Map your CRA technical documentation and SBOMs directly into your DORA third-party risk management workflow.
- Harmonize Reporting: Build a single “regulatory clock” to handle both the 4-hour DORA incident window and the 24-hour CRA vulnerability window.
- Continuous Validation: Use automated testing to prove operational resilience for DORA while simultaneously verifying product safety for the CRA.
- Executive Alignment: Ensure your management body understands that CRA product compliance is a prerequisite for DORA organizational resilience.
Turning Compliance into Performance
A unified strategy does more than just avoid fines. It creates a measurable competitive advantage. By being “CRA-ready” today, software vendors make themselves the safest choice for DORA-regulated banks. Likewise, financial entities that demand CRA-compliant products significantly reduce their own operational risk profiles.
Ultimately, 2026 is the year of transparency. Whether you are building software or managing a bank, your ability to provide real-time, technical proof of security is your most valuable asset. Do not wait for the next deadline. Align your product safety with your organizational resilience today to build a truly secure digital future.
Conclusion
Navigating the EU’s cybersecurity landscape in 2026 requires more than just meeting deadlines. It demands a fundamental shift in how your business integrates security into its daily operations. Consequently, the overlap between DORA and the CRA is no longer just a legal theory; it is a critical business pivot.
Your Next Steps for 2026 Compliance
- Bridge the Gaps: Identify where your product’s technical documentation can serve as evidence for DORA’s organizational audits.
- Test the Clocks: Ensure your incident response teams can meet both the 4-hour DORA and 24-hour CRA reporting windows simultaneously.
- Leverage Transparency: Use your CRA-mandated SBOM as a competitive tool to gain trust within the regulated financial market.
Because the regulatory landscape is shifting so rapidly, staying ahead of the curve is vital. For practical advice on moving from theory to implementation, read this guide on how to prepare for the CRA.
In summary, DORA secures the foundation of the financial sector, while the CRA secures the digital tools that build it. Therefore, aligning these two regulations today is the only way to ensure your organization remains resilient, compliant, and competitive tomorrow.
Are you ready for CRA?
With the CRA Framework in SAMMY, you can assess CRA compliance for your different products. The questions and quality criteria give you a complete checklist of everything that is required by CRA. SAMMY also makes it easy to compare products groups, manage compliance roadmaps and collaborate with team members.
Find out more about the SAMMY tool for CRA assessments.